Israeli Airstrike on Nasser Hospital in Gaza Kills Six, Around 20 Injured
GAZA, November 12, 2026: An Israeli airstrike hit the Nasser Medical Complex in Khan Younis, southern Gaza, killing…
PAKISTAN | INTERNATIONAL | TECHNOLOGY
 Trending #1
GAZA, November 12, 2026: An Israeli airstrike hit the Nasser Medical Complex in Khan Younis, southern Gaza, killing…
 Trending #2
Proofpoint’s BluePhishing proof of concept explores how malicious agent blueprint consent could lead to unauthorized Microsoft Entra identities and access.
 Trending #3
Huntress says attackers left webshells, a miner and a Python implant on three AhsayCBS servers at one organization after exploiting two backup-management vulnerabilities.
 Trending #4
ESET reports that attackers used DNS manipulation and insecure Sogou Input Method requests to deliver DarkVigil. Tencent addressed the weakness in version 16.10.

8 Life-Changing AI Healthcare Solutions Worth Watching AI Healthcare Solutions is moving from a trend to a working…

Smart AI Cybersecurity Practices to Protect Modern Teams AI Cybersecurity is moving from a trend to a working…
Generative AI in Education is moving from a trend to a working priority for educators, students, and institutions…
Anthropic’s planned IPO is one of the most important technology-market events of 2026. The company behind Claude is…
AI agents are becoming one of the most talked-about technologies in 2026. For the last few years, most…
Executive Summary The software industry has fundamentally shifted from Generative Assistance to Autonomous Agentic Orchestration. Instead of relying…
Microsoft Corp has initiated one of the largest corporate restructuring efforts in the tech sector extending voluntary exit…

Artificial Intelligence is transitioning from passive output generation to autonomous goal directed execution. Early generative models relied entirely…

The technology landscape is undergoing a rapid transition toward autonomous agentic workflows on device silicon acceleration and resilient…

The rapid evolution of consumer devices cloud infrastructure and artificial intelligence is fundamentally reshaping how people and enterprises…

The rapid evolution of modern computing technologies is driving a profound structural shift across global enterprise ecosystems. Organizations…

The global technology ecosystem is undergoing a major structural shift as recent enterprise announcements highlight advancements in enterprise…

Proofpoint’s BluePhishing proof of concept explores how malicious agent blueprint consent could lead to unauthorized Microsoft Entra identities and access.

Huntress says attackers left webshells, a miner and a Python implant on three AhsayCBS servers at one organization after exploiting two backup-management vulnerabilities.

ESET reports that attackers used DNS manipulation and insecure Sogou Input Method requests to deliver DarkVigil. Tencent addressed the weakness in version 16.10.

Git 2.56.1 and patched maintenance releases address six security issues, including CVE-2026-111760, which can allow code execution during a crafted recursive clone.
NEAR AI says an SGLang vulnerability gave an attacker access to an inference server and related systems. The company has revoked exposed keys and restored its Cloud service.

ConnectWise is investigating unauthorized access to ScreenConnect partner accounts and has disabled five third-party extensions as a precaution. Huntress reports affected MSPs and customer endpoints.
Vates says an authentication bypass in Xen Orchestra is being actively exploited. Administrators should update, restrict management access and investigate possible compromise.

Microsoft says CVE-2026-124194 is being exploited and can expose authentication information when a user opens a crafted message file. Security updates are available.

Debian and Ubuntu have issued fixes for CVE-2026-109518, an APT package-verification flaw that could enable root-level code execution under specific conditions.

CISA has flagged an exploited Cisco BroadWorks vulnerability that can expose sensitive configuration files. Cisco lists RI.2026.07 as the first fixed release.

JVN reports exploitation of CVE-2026-111793 in Openwave Webtop Media Transcoder. Administrators should identify affected versions and follow vendor upgrade guidance.
OPSSHIELD says a fake cPGuard update ran on approximately 2,950 servers. The company has issued clean updates and urged administrators to rotate potentially exposed credentials.

GAZA, November 12, 2026: An Israeli airstrike hit the Nasser Medical Complex in Khan Younis, southern Gaza, killing…
Proofpoint’s BluePhishing proof of concept explores how malicious agent blueprint consent could lead to unauthorized Microsoft Entra identities and access.
Huntress says attackers left webshells, a miner and a Python implant on three AhsayCBS servers at one organization after exploiting two backup-management vulnerabilities.
ESET reports that attackers used DNS manipulation and insecure Sogou Input Method requests to deliver DarkVigil. Tencent addressed the weakness in version 16.10.
Git 2.56.1 and patched maintenance releases address six security issues, including CVE-2026-111760, which can allow code execution during a crafted recursive clone.
NEAR AI says an SGLang vulnerability gave an attacker access to an inference server and related systems. The company has revoked exposed keys and restored its Cloud service.
ConnectWise is investigating unauthorized access to ScreenConnect partner accounts and has disabled five third-party extensions as a precaution. Huntress reports affected MSPs and customer endpoints.
Vates says an authentication bypass in Xen Orchestra is being actively exploited. Administrators should update, restrict management access and investigate possible compromise.
Microsoft says CVE-2026-124194 is being exploited and can expose authentication information when a user opens a crafted message file. Security updates are available.
Debian and Ubuntu have issued fixes for CVE-2026-109518, an APT package-verification flaw that could enable root-level code execution under specific conditions.
CISA has flagged an exploited Cisco BroadWorks vulnerability that can expose sensitive configuration files. Cisco lists RI.2026.07 as the first fixed release.
JVN reports exploitation of CVE-2026-111793 in Openwave Webtop Media Transcoder. Administrators should identify affected versions and follow vendor upgrade guidance.

ISLAMABAD, November 12, 2026: The Pakistan Minerals Investment Forum 2026 (PMIF26) has opened in Islamabad, bringing together government…

A deadly attack on a police contingent in Kohat district of Khyber Pakhtunkhwa (KP) has resulted in the…
Date: November 11, 2026 Pakistan’s political tensions have intensified following former prime minister Imran Khan’s transfer from Adiala…

Date: November 11, 2026 Pakistan’s security situation faced another serious challenge on Wednesday after militants attacked police vehicles…

The revised rates became effective on November 11, 2026. The Pakistan petrol price has been reduced to Rs338…

Date: November 11, 2026 A serious incident at Pakistan’s major hydropower development site has raised fresh questions about…
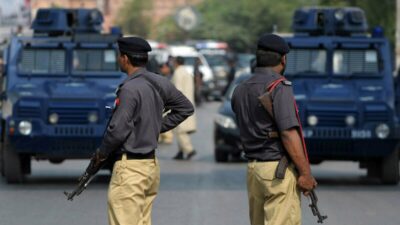
Kohat Attack has become a major security development in Pakistan on November 11, 2026, after militants ambushed vehicles…

Publication Date: November 11, 2026 Pakistan has made a major change in its federal financial arrangements after the…

Publication Date: November 11, 2026 A deadly shooting in Balochistan’s Noshki district has left three people dead after…
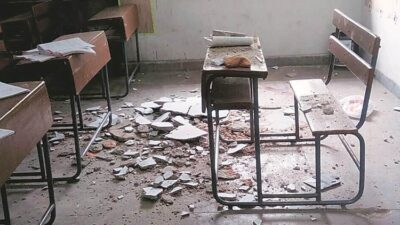
Publication Date: November 11, 2026 A disturbing education-related incident has emerged from Faisalabad after a classroom roof collapsed…

Publication Date: November 11, 2026 Pakistan has been struck by another deadly security incident after a devastating Kohat…
Generative AI in Education is moving from a trend to a working priority for educators, students, and institutions…
Proofpoint’s BluePhishing proof of concept explores how malicious agent blueprint consent could lead to unauthorized Microsoft Entra identities and access.
Huntress says attackers left webshells, a miner and a Python implant on three AhsayCBS servers at one organization after exploiting two backup-management vulnerabilities.
ESET reports that attackers used DNS manipulation and insecure Sogou Input Method requests to deliver DarkVigil. Tencent addressed the weakness in version 16.10.
Git 2.56.1 and patched maintenance releases address six security issues, including CVE-2026-111760, which can allow code execution during a crafted recursive clone.
NEAR AI says an SGLang vulnerability gave an attacker access to an inference server and related systems. The company has revoked exposed keys and restored its Cloud service.
ConnectWise is investigating unauthorized access to ScreenConnect partner accounts and has disabled five third-party extensions as a precaution. Huntress reports affected MSPs and customer endpoints.
Vates says an authentication bypass in Xen Orchestra is being actively exploited. Administrators should update, restrict management access and investigate possible compromise.
Microsoft says CVE-2026-124194 is being exploited and can expose authentication information when a user opens a crafted message file. Security updates are available.
Debian and Ubuntu have issued fixes for CVE-2026-109518, an APT package-verification flaw that could enable root-level code execution under specific conditions.
CISA has flagged an exploited Cisco BroadWorks vulnerability that can expose sensitive configuration files. Cisco lists RI.2026.07 as the first fixed release.
JVN reports exploitation of CVE-2026-111793 in Openwave Webtop Media Transcoder. Administrators should identify affected versions and follow vendor upgrade guidance.
OPSSHIELD says a fake cPGuard update ran on approximately 2,950 servers. The company has issued clean updates and urged administrators to rotate potentially exposed credentials.