Japan | November 6, 2026
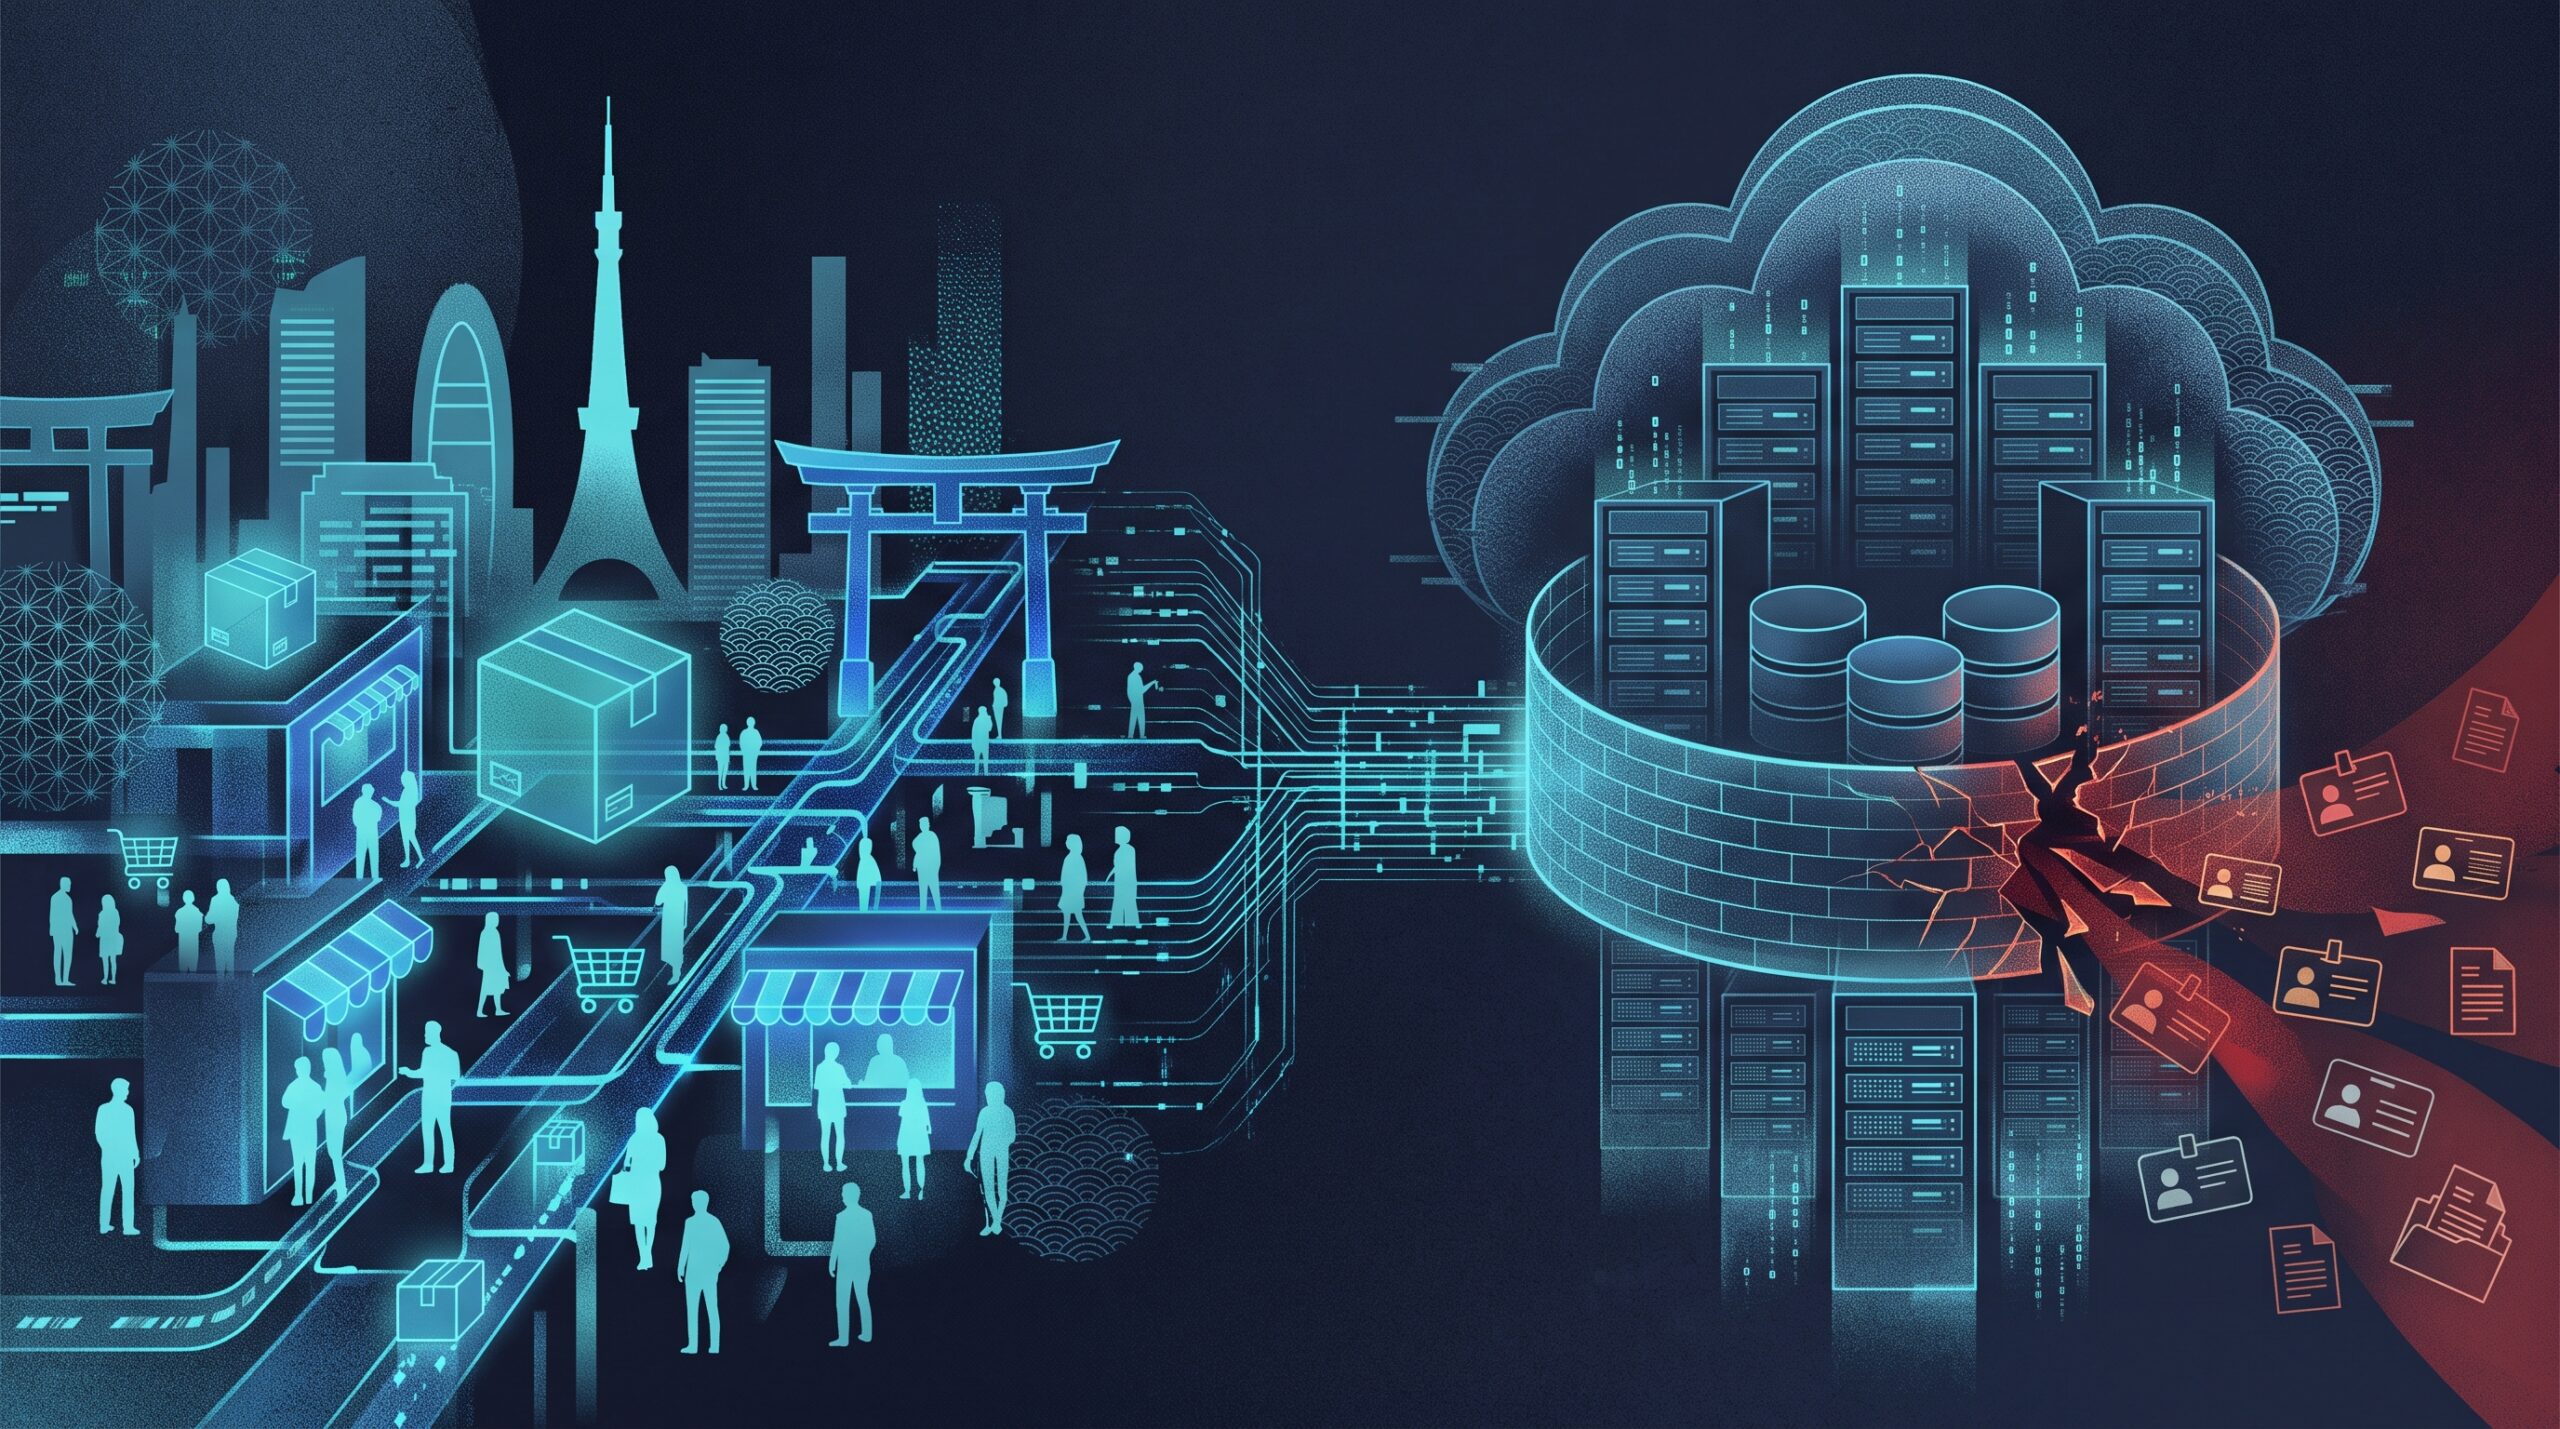
A cyber incident involving Iris Plaza, the official online shopping platform operated by Iris Plaza Co., may have exposed personal information associated with approximately 7.7 million customer records in Japan. The company disclosed the potential exposure on November 5 after investigating unauthorized access to an external cloud service used to store customer information.
The affected information may include names, residential addresses, telephone numbers, email addresses and other personal details. Data associated with approximately 5.8 million registered and former members was potentially exposed, alongside information relating to approximately 1.9 million non-members who had purchased products or entered campaigns.
The company has emphasized that the 7.7 million figure represents the scale of information stored in the affected environment, not a confirmed number of people whose information was actually obtained. The investigation into the extent of the exposure remains ongoing.
The Iris Plaza data breach has also raised questions about the protection of customer information held through external cloud services. Although the company says credit-card information was not stored in the affected environment, the potentially exposed personal details could still create risks for customers if misused.
What Happened in the Iris Plaza Data Breach?
Iris Plaza operates the official online shopping website associated with Japanese consumer-products company Iris Ohyama. Customers use the platform to purchase household products and other goods. The service also holds information connected to registered accounts, previous purchases and campaign participation.
According to the company’s November 5 announcement, an incident involving an external cloud service was identified on October 28, 2026. The company discovered a suspicious file in the cloud environment it used and immediately suspended the Iris Plaza website and related systems while it began investigating.
The investigation confirmed unauthorized access by a third party. Iris Plaza subsequently reported the incident publicly on October 29, initially explaining that it had identified suspicious activity and was examining the circumstances.
Further investigation led to the November 5 update. The company said that information stored in the external cloud service may have been disclosed outside the organization. It also said that the stored data may have been viewed or obtained by an unauthorized party.
The Iris Plaza data breach therefore involves a confirmed unauthorized-access incident and a potential exposure of personal information. However, the company has not confirmed that every record in the affected environment was copied or accessed.
That distinction is important. The existence of a large database in an affected environment does not automatically establish that every record was extracted. The actual number of affected people and the volume of information accessed remain subjects of the investigation.
The 7.7 Million Figure: Who Could Be Affected?
The company’s November 5 disclosure divided the potentially affected information into two main groups: registered-member data and non-member data.
| Data category | Approximate number | Potentially affected information |
| Members, including former members | 5.8 million | Names, addresses, telephone numbers, email addresses, gender, passwords and dates of birth, among other information |
| Non-members | 1.9 million | Names, addresses, telephone numbers and email addresses |
| Combined reported scope | 7.7 million | Potentially exposed personal information |
The member category includes former members, not only people who currently maintain active accounts. The non-member category includes people who purchased products without registering an account and individuals whose information was collected through campaign applications.
This means that people who no longer use Iris Plaza, or who never created a permanent shopping account, may still fall within the potentially affected population.
However, the company has cautioned that not every person necessarily had every listed data field stored in the affected environment. The information associated with each individual depends on their registration and interaction history.
The Iris Plaza data breach should therefore not be described as a confirmed leak of 7.7 million complete customer profiles. The company has identified approximately 7.7 million people’s worth of stored personal information as potentially affected, but it is still investigating the actual number of records accessed or taken.
Password Information and Credit-Card Data
One of the most important aspects of the disclosure concerns the types of information stored in the affected environment.
The member database included password information. Iris Plaza stated that passwords and certain other fields were encrypted. It also clarified that former members’ records did not include password information.
The company has not provided enough technical detail in its public announcement to establish the encryption method, password-storage design or whether any password material was successfully obtained in a usable form. Encryption is an important protective measure, but its presence alone does not establish that all affected credentials are beyond risk.
Customers who reused the same password on other websites should therefore take the company’s precautionary advice seriously. If credentials were exposed or later recovered, password reuse could allow an attacker to attempt access to unrelated services.
There is a separate and important distinction concerning payment information. Iris Plaza said credit-card information was not stored in the particular external cloud service involved in the incident and confirmed that such information was not affected by this unauthorized access.
That statement should not be expanded into a claim that every payment-related system across the wider Iris group was investigated and found unaffected. The company’s disclosure specifically addresses the affected cloud environment.
For now, the Iris Plaza data breach is primarily a personal-information exposure incident. The company has not reported that credit-card numbers were included in the affected data.
Timeline: From Suspicious File Discovery to Public Disclosure
The company’s announcements establish a short initial response timeline, followed by additional investigation.
October 28, 2026: Suspicious file discovered
Iris Plaza identified a suspicious file in an external cloud service it used. The company immediately suspended the Iris Plaza website and related systems and began investigating the incident.
The discovery of a suspicious file was the event that triggered the company’s response. The public disclosure does not explain who created the file, how it arrived in the environment or what activity preceded its discovery.
October 29, 2026: Unauthorized access confirmed and first notice issued
Following its initial investigation, the company confirmed unauthorized access by a third party. It issued its first public notice and reported the incident to the police and Japan’s Personal Information Protection Commission.
The company also took steps to block the unauthorized access route and continued examining the affected systems.
November 5, 2026: Potential exposure of 7.7 million records disclosed
The second public update provided a clearer picture of the potential data exposure. The company said information stored in the external cloud service may have been viewed or obtained and disclosed the approximate 5.8 million member and 1.9 million non-member figures.
It also explained which categories of personal information may have been involved and clarified that credit-card information was not stored in the affected cloud environment.
November 6, 2026: Investigation remains ongoing
As of November 6, the company’s disclosed position remains that the actual number of affected people and records has not been determined. It has not publicly established the technical intrusion method or announced a final account of the information obtained.
The timeline shows that the company moved to suspend the affected services when it discovered suspicious activity. It does not, by itself, establish when the unauthorized access began or how long an attacker may have had access.
External Cloud Services and the Wider Security Challenge
The Iris Plaza data breach highlights a security challenge that affects organizations using external technology services: sensitive information can be exposed through systems that are not necessarily operated entirely within a company’s own infrastructure.
Businesses increasingly rely on cloud platforms and external providers to store, process and manage information. These arrangements can support business operations, but they also create dependencies that must be included in an organization’s security planning.
An organization remains responsible for understanding what information it places in an external environment, who can access it, how access is controlled and how suspicious activity is detected.
The Iris Plaza announcement identifies the affected environment as an external cloud service. However, it does not disclose the provider’s identity or explain whether the incident resulted from compromised credentials, an improperly configured service, a software vulnerability or another access-control weakness.
Without those details, it would be premature to assign the incident to a particular technical failure or blame the cloud provider. Unauthorized access to a cloud environment can occur through several different routes, and the available public information does not establish which one applied here.
The incident nevertheless demonstrates why companies need visibility across their external technology arrangements. Security reviews should include account permissions, authentication controls, logging, monitoring, data retention and the process for responding to suspicious activity.
The Iris Plaza data breach also illustrates why organizations should understand exactly which customer information is held by external services. A company may operate the customer-facing website while data supporting that service is stored or processed elsewhere.
That separation can make incident response more complicated. Investigators may need to examine the service provider’s environment, access records and system configuration before determining the full scope of an incident.
Related Services Also Suspended
The response extended beyond the main Iris Plaza shopping website.
The company said its home-fashion website, SIMPLE STYLE, was suspended from October 28 as a precaution. Related services operated by Iris Tech Service, including home-appliance subscription and furniture or appliance delivery and installation services, were also suspended and stopped accepting new applications.
Importantly, Iris Plaza stated that unauthorized access and information leakage had not been confirmed in those two related service areas at the time of its announcement.
Their suspension should therefore be understood as a precautionary measure, not evidence that the same data exposure affected every service.
The company said the affected services would be addressed separately and that reopening information would be provided when available. The main Iris Plaza website would be considered for reopening after the cause had been identified and measures to prevent a recurrence had been implemented.
The interruption also demonstrates that a security incident involving one external environment can have operational consequences beyond the specific data store under investigation. Companies may suspend connected services to reduce uncertainty and limit the possibility of further exposure while they investigate.
What Iris Plaza Customers Should Do
Iris Plaza said it would contact potentially affected customers individually by email and other appropriate means, based on the results of its investigation. Customers should monitor official communications, while remaining alert to messages that attempt to exploit the incident.
The company has specifically warned that it will not ask customers to provide passwords, PINs, authentication codes or other sensitive information as part of its notification process. It also said it will not ask customers to enter those details through links contained in email or SMS messages.
Customers should consider the following precautions:
- Change reused passwords: If the same password was used for Iris Plaza and another online service, change it on the other service. Use a unique password for each account.
- Be cautious with unexpected messages: Do not open suspicious attachments, follow unfamiliar links or reply to messages claiming to provide breach-related assistance.
- Do not disclose authentication codes: Legitimate incident notifications should not require customers to send passwords, PINs or one-time verification codes.
- Check official announcements: Use the company’s established website and contact channels rather than links supplied in unexpected messages.
- Watch for targeted impersonation: Names, addresses, telephone numbers and email addresses can make fraudulent messages appear more convincing.
- Contact relevant providers if concerned: If a customer believes credentials have been entered into a suspicious website, they should contact the affected service directly and secure the account.
These precautions are useful even for people who have not received an individual notification. The company has not yet completed its investigation or established the final list of affected individuals.
What Remains Unknown?
Several important questions remain unanswered.
First, the company has not disclosed the precise technical method used to gain unauthorized access to the external cloud service. There is no confirmed public explanation of whether the incident involved stolen credentials, a vulnerability, a configuration problem or another method.
Second, the number of records actually viewed or obtained remains uncertain. The 7.7 million figure describes the stored information potentially affected, not a verified count of extracted records or confirmed victims.
Third, the company has not identified the external cloud provider in its public announcement. It has also not disclosed a complete technical account of the suspicious file or the activity detected in the environment.
Finally, the investigation has not established whether any of the potentially exposed information has been misused. The company said it had received no reports of related unauthorized use or financial damage at the time of its November 5 disclosure.
These gaps matter because the final impact of a data incident depends on more than the size of the database involved. The information actually accessed, the security controls protecting it and any subsequent misuse all affect the level of risk to customers.
Conclusion: A Major Exposure Still Under Investigation
The Iris Plaza data breach is a significant security incident because it potentially involves personal information associated with approximately 7.7 million people in Japan, including former members and non-members.
The company’s response included suspending the affected website, blocking the unauthorized access route, reporting the incident to relevant authorities and beginning customer notifications. It has also said that credit-card information was not stored in the affected cloud environment.
But important questions remain. The actual number of affected people, the intrusion method, the identity of the external cloud provider and the full extent of any information obtained have not been established publicly.
The next important developments will be the company’s findings on the scope and cause of the incident, its explanation of the safeguards being introduced and its decision on when affected services can safely resume.
Until those details are available, customers should treat unexpected breach-related messages with caution, avoid reusing passwords and rely on official company communications for updates.
Source note: This report draws on the November 5, 2026 disclosure from Iris Ohyama and Iris Plaza, together with reporting by Kyodo News and FNN Prime Online. The number of records potentially affected should not be interpreted as a confirmed count of people whose information was obtained. The intrusion method, actual exposure scope and any subsequent misuse remain under investigation.
NewsFlayer — Your trusted source for cybersecurity news, digital threats and technology developments.