
Singapore | November 7, 2026
A critical security flaw in the Metabase business-intelligence platform is under active exploitation, prompting Singapore’s Cyber Security Agency (CSA) to urge organizations to patch vulnerable systems immediately. Tracked as CVE-2026-72898, the Metabase vulnerability carries a maximum CVSS v3.1 score of 10.0 and could allow an unauthenticated remote attacker to inject SQL into the platform’s application database and obtain administrator access.
The warning is significant because Metabase is commonly used to connect business users with operational databases, data warehouses and reporting systems. An attacker who takes control of a Metabase instance may be able to access stored database credentials and information available through its connected data sources, depending on the permissions and configuration of the affected environment.
The Singapore CSA issued its alert on November 4, confirming that the flaw was being actively exploited and that proof-of-concept exploit code was publicly available. Metabase had disclosed the vulnerability and released security updates in August, after identifying an attack against its cloud service.
The Metabase vulnerability therefore represents more than a software-update concern. Organizations operating exposed self-hosted instances need to patch, investigate possible compromise and assess whether credentials or connected data sources may have been exposed.
Singapore Warns of Active Exploitation
In its November 4 security alert, Singapore’s CSA described CVE-2026-72898 as a critical vulnerability affecting multiple Metabase release branches. The agency said successful exploitation could allow an unauthenticated remote attacker to inject arbitrary SQL into the Metabase application database and gain administrator access to the connected instance.
The advisory also confirmed active exploitation and the public availability of proof-of-concept code. Those details increase the urgency for administrators because attackers do not necessarily need to develop their own exploit from scratch before attempting to target vulnerable systems.
The Metabase vulnerability had already been identified and addressed by the vendor in August. However, the publication of patches does not automatically protect installations that remain on vulnerable releases. Self-hosted deployments may continue to be exposed when administrators delay updates, overlook older instances or fail to identify systems operating outside their central software-management process. The Metabase vulnerability remains a priority for defenders because public exploit availability can increase pressure on organizations that have not completed the required updates.
The CSA recommended that organizations update affected products to patched versions immediately. It also advised administrators who cannot upgrade at once to temporarily block access to the affected password-reset endpoint.
The agency’s warning is particularly relevant to organizations that make their Metabase installations accessible from the public internet. A publicly reachable service gives remote attackers an opportunity to attempt exploitation without first obtaining legitimate application credentials.
What the Metabase Vulnerability Allows Attackers to Do
CVE-2026-72898 is an SQL injection vulnerability associated with Metabase’s password-reset functionality. SQL injection occurs when an application handles input in a way that allows an attacker to interfere with database queries. Depending on the weakness and the privileges of the database account, the attacker may be able to read, modify or otherwise manipulate stored information.
In this case, the affected endpoint is:
POST /api/session/reset_password
The vendor’s security advisory explains that an unauthenticated remote attacker can use the weakness to inject arbitrary SQL into the Metabase application database. The resulting access can allow the attacker to obtain administrator privileges within the affected instance. This makes the Metabase vulnerability particularly serious for deployments where the application database contains sensitive account information or configuration data.
The distinction between the Metabase application database and the business databases connected to it is important. The application database stores information used to operate the Metabase service, including account and configuration data. Metabase can also maintain connections to external databases and data warehouses used to generate dashboards, reports and analytical queries.
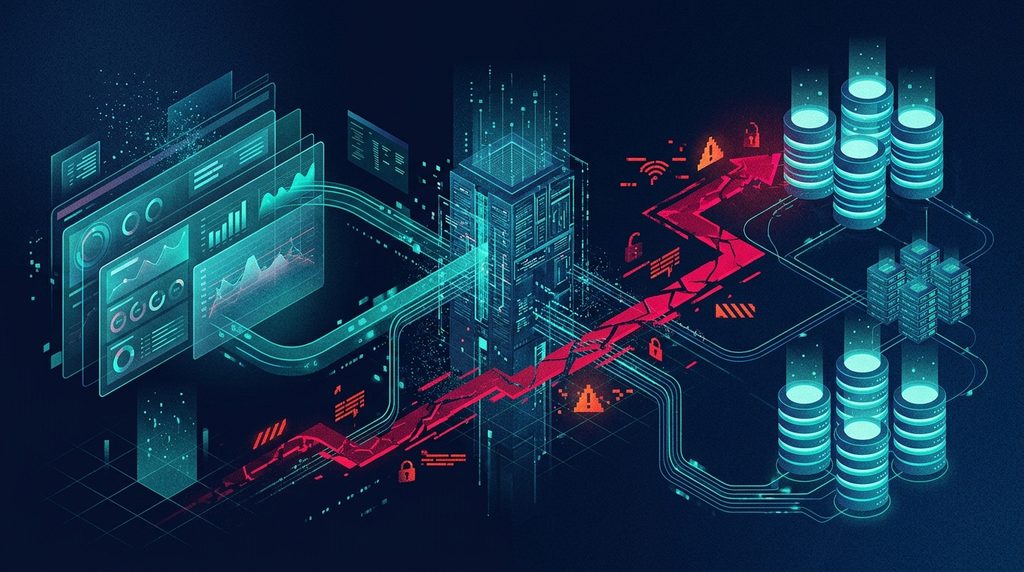
An attacker who gains administrative access may be able to change application settings, access stored credentials for connected databases and retrieve information available through those connections. The potential exposure therefore depends on the permissions assigned to the database connections, the data they can reach and the security controls surrounding the wider environment.
The Metabase vulnerability does not automatically mean that every database connected to an affected installation has been compromised. Nor does the advisory establish that all information accessible to a Metabase administrator was necessarily extracted in every exploitation attempt. Organizations must investigate their own logs, credentials, query history and connected systems to determine whether unauthorized activity occurred.
Why the CVSS 10.0 Score Matters
The vulnerability has a CVSS v3.1 base score of 10.0, the highest possible rating under that scoring system. The score reflects a combination of characteristics that make exploitation particularly serious.
The attack can be conducted over a network, requires low attack complexity, does not require prior privileges and does not depend on a victim interacting with a malicious link or file. The published scoring assessment also identifies high potential impacts on confidentiality, integrity and availability.
In practical terms, an attacker does not need an existing Metabase account to attempt exploitation of a vulnerable, reachable instance. If the attack succeeds, the resulting administrator access could affect the confidentiality of information, the integrity of application settings and the availability of the service.
A maximum severity score describes the technical potential of the vulnerability; it is not a measurement of how many organizations have been compromised. The actual consequences depend on whether an installation is vulnerable and reachable, whether exploitation succeeds, what access the instance possesses and how quickly defenders detect suspicious activity. For organizations with exposed systems, the Metabase vulnerability should therefore be handled as an urgent remediation issue rather than a routine maintenance task.
The Metabase vulnerability also illustrates why business-intelligence platforms deserve the same attention as other systems that hold privileged access to organizational information. Although these tools are often deployed to make data easier to analyze, their database connections can make them valuable targets.
Metabase Disclosed a Cloud Security Incident in August
Metabase publicly disclosed the security issue on August 6, 2026. In its announcement, the company said its Metabase Cloud service had been attacked by someone using an unknown zero-day vulnerability affecting versions 1.58 and above.
The company said it blocked the endpoints used in the attack, identified the vulnerability and quickly patched it. Metabase also stated that cloud customers’ instances had already been upgraded and protected against the flaw.
The vendor warned that self-hosted installations could remain vulnerable. It explained that an attacker who gained access could inject SQL into the application database, obtain administrator access, change configuration settings, steal stored credentials for connected databases and access or export data available through those connections.
This distinction matters for organizations using the hosted service and those managing their own infrastructure. Metabase said its cloud instances had been patched, while self-hosted customers were instructed to update their own deployments. Administrators should not assume that a vendor’s action on its hosted environment automatically updates a separately managed installation.
The August disclosure also means that the vulnerability was not first identified in November. The Singapore alert is a later public warning about active exploitation and proof-of-concept availability, reinforcing the need for organizations to verify that their systems were patched and checked after the initial disclosure.
A Confirmed Downstream Incident Shows the Potential Consequences
The risks are not limited to theoretical attack scenarios. Cloud platform provider Scalingo later reported that attackers successfully exploited an internal Metabase instance affected by CVE-2026-72898.
In its security bulletin, Scalingo said information relating to approximately 90,000 individuals had been exfiltrated from an internal analytics data warehouse. The disclosed categories included identity and contact information, account-related details, GitHub profile information, limited billing-related information and technical metadata associated with services and databases.
Scalingo said it had found no evidence that attackers accessed customer production applications, production databases or data stored within those workloads. The company took the affected Metabase service offline, deployed the security fix, began credential rotation and reported that it had completed a forensic investigation.
The incident demonstrates how a compromise of an analytics platform can create consequences beyond the platform itself. Business-intelligence services may contain information about customers, accounts, infrastructure and internal operations, even when they are not the primary systems used to deliver a company’s services.
However, the Scalingo disclosure should be understood as one organization’s reported incident. It does not establish that 90,000 people were affected by the vulnerability across all Metabase deployments, nor does it provide a global estimate of successful attacks. The Metabase vulnerability demonstrates why organizations must investigate the data connections and credentials available to an analytics platform after a suspected compromise.
The Metabase vulnerability is especially concerning where an analytics instance has broad database permissions or stores credentials that allow access to sensitive environments. Organizations should therefore examine the permissions and data exposure associated with each connection rather than treating the Metabase server as an isolated reporting tool.
Which Metabase Versions Are Affected?
The Singapore CSA advisory lists affected releases across several Metabase version branches. The vendor’s security advisory identifies the following minimum patched releases:
| Affected branch | Minimum patched release |
| 0.58.x | 0.58.24 |
| 0.59.x | 0.59.21 |
| 0.60.x | 0.60.17 |
| 0.61.x | 0.61.11 |
| 0.62.x | 0.62.9 |
| 0.63.x | 0.63.5 |
Administrators should update to the appropriate patched point release for the branch they operate, or to a later supported release. Metabase stated that versions below 0.58 were not affected by this particular issue.
The advisory also lists corresponding Enterprise version branches, including 1.58 through 1.63, with the same minimum patch numbers for each branch. Administrators should check the vendor’s current security advisory and release information to confirm the correct update for their deployment.
Organizations should inventory all Metabase installations rather than checking only their primary production server. Development, testing, staging and departmental instances can be overlooked, particularly where individual teams deploy analytics tools independently.
The Metabase vulnerability may remain a risk wherever an affected release is still running. Updating only the most visible instance is not sufficient if another internet-accessible deployment remains unpatched.
What Administrators Should Do Immediately
The first priority is to identify affected deployments and install the relevant security update. Metabase and Singapore’s CSA both recommend immediate patching. If an organization cannot upgrade straight away, the vendor and CSA identify blocking access to /api/session/reset_password as a temporary workaround.
That workaround should not be treated as a permanent substitute for installing the security fix. Administrators should also confirm that the endpoint is no longer exposed to unauthorized remote access after the patch and review the configuration of any reverse proxies, gateways and network controls protecting the service.
For publicly accessible instances, Metabase recommends several post-upgrade security checks:
- Revoke active sessions: In the Metabase application database, remove existing rows from the core_session table as directed by the vendor.
- Review administrator accounts: Check for unexpected accounts, privilege changes or modifications to existing administrator access.
- Inspect API keys: Identify unrecognized keys and remove those that were not legitimately created.
- Rotate connected-database credentials: Replace credentials used by Metabase to access external databases and data warehouses.
- Review database logs: Look for unusual access, unexpected queries, data exports or activity that cannot be linked to legitimate users.
- Examine Metabase activity: Check application activity and query history for suspicious or unauthorized operations.
Metabase also published an attack pattern that administrators can look for in application and server ingress logs. The vendor said a POST /api/session/reset_password request returning a 400 status code followed by a GET /api/user/current request returning a 200 status code may indicate that an instance has been compromised.
This pattern is a warning sign, not a complete forensic test. Administrators should preserve relevant logs and investigate suspicious events in context rather than assuming that the absence of this exact sequence proves a system is clean.
Where there is evidence of unauthorized access, organizations should follow their incident-response procedures, preserve forensic evidence and assess whether information in connected databases may have been accessed. Credential rotation should include relevant service accounts and other secrets that could have been exposed through the Metabase environment.
Why Business-Intelligence Platforms Are High-Value Targets
Business-intelligence systems occupy an important position between employees and the databases that support business operations. They make it easier to combine information, build dashboards and distribute reports, but they can also hold access to multiple data sources in one place.
That position can make an analytics platform an attractive target. A compromised instance may reveal information about customer activity, internal performance, business operations and technical infrastructure. If its database connections have broad permissions, an attacker may gain a route to information that is not directly exposed through the public-facing application.
The risk is not unique to Metabase. Organizations using analytics, reporting and data-integration platforms should apply the same security principles used for other privileged infrastructure. These include restricting administrative access, limiting database permissions, protecting secrets, monitoring unusual queries and maintaining an accurate inventory of deployed services.
The Metabase vulnerability also highlights the importance of reviewing access granted to analytics tools. A reporting application should not automatically receive unrestricted access to every table or database simply because users want convenient dashboards. Where possible, organizations should use narrowly scoped service accounts and separate access to sensitive datasets.
Internet exposure is another important consideration. Administrative and password-reset functions should not be unnecessarily reachable from untrusted networks. Network restrictions, authentication controls and monitoring can reduce opportunities for abuse, although they do not replace patching a vulnerable application.
A Patch Is Only the First Step
The Singapore CSA warning reinforces a wider lesson for organizations that rely on business-intelligence platforms: a security update must be followed by a review of what may have happened before the update was installed.
Metabase released fixes in August, but the later Singapore alert confirms that exploitation remained an active concern in November. Public proof-of-concept availability can make it easier for additional attackers to test exposed systems, while unpatched installations may remain vulnerable long after a vendor has published a correction.
Organizations should therefore combine immediate software updates with credential rotation, session revocation, administrator-account reviews and examination of connected database activity. If suspicious access is identified, incident responders should assess the scope of exposure and determine whether notification obligations apply.
For companies using Metabase to connect business users with sensitive operational data, the issue is a reminder that analytics infrastructure can carry significant security responsibilities. Protecting the dashboards alone is not enough; the credentials, databases and information behind them must also be secured.
Source note: This report draws on the Cyber Security Agency of Singapore’s November 4, 2026 alert, Metabase’s official security update and GitHub advisory, and technical reporting from Wiz and Scalingo’s incident disclosure. The reported Scalingo impact applies to that organization’s investigation and should not be interpreted as a global estimate of affected Metabase users.
NewsFlayer — Your trusted source for cybersecurity news, digital threats and technology developments.